

Key Attestation Demo
by Xingchen & Rikka
4.8
- Safety
- 100% Safe
- Category
- Libraries & Demo
- Ratings
- 4.8
- Price
- Free
- Download
- 100.00K
This app is secure, reliable, free to install, and offers fast downloads without any risks or malware.
Screenshots
 Analysis by Getfullapps
Key Attestation Demo is a small Android utility with a very specific purpose: it lets me examine the Android system’s Key Attestation capability instead of trying to be an everyday productivity tool. That narrow focus is exactly what makes it useful. If you develop, test, or study Android security, it offers a direct way to see how a device reports information about cryptographic keys and the environment protecting them.
I would not recommend it as a casual app for someone looking for a file manager, privacy dashboard, or general device diagnostic tool. Its value appears when you already have a question about hardware-backed key security and want a practical demonstration rather than a paragraph of documentation. The app is free, rated for Everyone, and comes from Xingchen & Rikka, a developer associated here with a technical demonstration rather than a broad consumer application.
What the app demonstrates and why it matters
The central capability is Android Key Attestation. In plain language, this is a way for an application or test process to ask the Android security system for evidence about a cryptographic key and the conditions under which that key was created or is being protected. The important point is that the app is not merely showing a random device-information page. It is demonstrating a security mechanism built into Android.
That distinction matters because ordinary software checks can be misleading. An app may read a model name, operating-system release, or other visible setting, but those values do not by themselves prove how securely a key is stored. Key Attestation is designed for a different question: can a relying service evaluate information signed by the Android keystore about a key and its security context?
In my view, the most useful lesson is that security claims need a chain of trust. A text label saying “secure” is easy to display. A cryptographic attestation is more meaningful because the result is tied to keys and signatures that can be examined by software designed to validate them. This demo makes that concept easier to approach on a real Android device.
The app belongs in the Libraries & Demo section, and that classification is appropriate. It is closer to a reference implementation or a learning instrument than a consumer utility. You install it to inspect a particular Android feature, not to leave it running all day or to replace another app you use regularly.
What I look for when using it
When I use a technical demo like this, I do not treat its screen as a final security verdict. I look at what the device reports, which parts are generated by Android’s keystore framework, and which conclusions require outside interpretation. That mindset is important here. The application can demonstrate the attestation process, but a displayed result still needs to be understood in the context of the device, the operating-system build, and the service that would ultimately verify it.
Articles to Explore Next

Uber Eats Makes Dinner Easier to Manage, but the Fees Add Up

Google Photos Turns a Camera Roll Into a Library You Can Find Your Way Through

Canva on Mobile: Adopt It for Quick Visuals, Test It for Demanding Work

Google Drive Keeps Work Moving Until It Doesn’t

Switching to Weather - By Xiaomi Means Relearning Your Forecast Routine

Ludo King and the Social Life of a Lucky Six
This is one of the app’s strengths for learners. It exposes a concept that is often hidden behind APIs and security documentation. Instead of only reading about attestation, I can use the demonstration to connect the terms with an actual device response. For a developer, that can make it easier to decide what needs to be checked in a prototype and what should be validated on a backend.
There is also a useful boundary here: Key Attestation is not the same thing as a complete security audit. It does not turn the app into a malware scanner, certify every installed application, or guarantee that a phone is safe for every purpose. I would avoid using it to make sweeping claims such as “this device is completely secure.” Its role is more focused and, because of that, more credible when used carefully.
How the demonstration works in practice
The practical experience is intentionally technical. After installing Key Attestation Demo, I approach it as a test bench: create or inspect the demonstration’s key-related output, read the information Android exposes, and consider what each field means. The useful workflow is not simply opening the app and accepting a green-looking result. It is comparing the reported details with the security requirement I am trying to understand.
For example, a developer investigating protected key storage may want to know whether the device can produce attestation information that a server could later validate. The demo helps make that workflow tangible. I can use it while reading the Android Key Attestation documentation, then return to the app to connect abstract terms with the output on my own phone.
A second practical use is troubleshooting. If a security-sensitive prototype behaves differently across two Android devices, a demonstration tool can help separate an application bug from a difference in keystore support or device configuration. I would record the results from each test, avoid changing several variables at once, and treat the app as one piece of evidence rather than the only diagnostic source.
That last point is especially important when testing older phones, modified software, or different manufacturer implementations. Android’s security hardware and system integration can vary. The app can reveal a result from the current environment, but it cannot make two devices behave identically. If a result surprises me, I would verify it against the Android version, device documentation, and the actual validation code used by the project.
The current release is version 1.5.0 and requires Android 7.0 or later. That makes it accessible to a reasonably broad range of Android devices, while still keeping the experience tied to the capabilities exposed by the operating system and hardware. A compatible Android version is only the entry requirement; the depth of the result can still depend on the particular phone.
A workflow I would recommend to developers
I would use the app in three passes. First, I would run the demonstration without changing anything and save the output for reference. Second, I would read the relevant Android documentation and mark which values describe the key, which relate to the attestation chain, and which concern the device environment. Third, I would compare the demonstration with the validation logic in my own project.
This prevents a common mistake: copying a field into an application decision without understanding its meaning. Attestation data is useful because it can support a policy, but the policy has to be designed first. A banking prototype, a test build, and a casual experiment may reasonably require different checks. The demo is most valuable when it encourages that careful thinking.
I would also keep a written record of the device and software context for every test. That is a simple but non-obvious habit that saves time later. If the output changes after a system update or on another phone, a note makes the difference explainable. Without that record, it is easy to assume that an application change caused a result that actually came from the device environment.
Another useful tip is to test the verification path separately from the display. Seeing attestation-related information on the phone is not identical to proving that a remote service can validate it correctly. If I were building a real product, I would use the demo to understand the input, then test the complete server-side verification process with controlled cases. That is where many practical mistakes appear.
The best real-world scenario
The strongest scenario is an Android developer building a service that needs to make risk-based decisions about the device creating or using a cryptographic key. Imagine a developer prototyping a sign-in flow for a sensitive application. The question is not simply whether the user has entered the right password. The service may also want evidence about the key’s origin and protection before trusting a particular operation.
In that situation, I would install Key Attestation Demo on test devices before writing a large amount of application code. It could help me understand what the Android environment can report, identify differences between test phones, and plan which checks belong on the server. The app would not replace the production security design, but it would make the early investigation more concrete.
This is also a good fit for an Android security course or a personal learning project. Reading about trust chains can feel abstract until I see how a key and its attestation-related information are connected. A student can use the app as a starting point for questions such as why signed evidence matters, why a server should validate rather than blindly trust client text, and why device capabilities affect security decisions.
For a support engineer, the scenario is slightly different. Suppose a test application works on one phone but fails on another when it requests a protected key. The demo may help establish whether the difference is related to Android’s key-management environment. I would still need logs and application-level testing, but this gives the investigation a more focused direction than repeatedly reinstalling the app.
The app is less useful for a normal phone owner who only wants to know whether their device is “safe.” That question is too broad for this demonstration. A person in that position would gain more from keeping Android updated, using reputable applications, reviewing account security, and following the guidance of the services they use. Installing this tool without a specific question could lead to confusion rather than reassurance.
What the results can and cannot tell you
The most responsible way to read the output is as evidence about a particular cryptographic and device-security mechanism. It can help me understand how Android presents attestation information and whether a test environment exposes the expected pathway. It cannot, by itself, inspect every layer of the phone or certify the behavior of an application that uses the result incorrectly.
This distinction also answers a question many users have: does installing the demo protect the phone? No. Its purpose is observation and experimentation. It does not become a security shield simply by being present. The benefit comes from what a developer or learner does with the information, especially when designing validation and handling unusual device conditions.
Another practical question is whether the app is useful without programming knowledge. A curious Android user can still open it and learn from the terminology, but the deeper value arrives when the output is read alongside Android security documentation. I would call it approachable as a demonstration, but not self-explanatory as a complete lesson. Someone unfamiliar with keystores, certificates, or verification may find the information dense.
Trade-offs, friction, and comparison with ordinary tools
The biggest trade-off is specialization. Key Attestation Demo does one technical job instead of offering a wide collection of device tests. That makes it more focused than general hardware-information apps, which may show processor details, memory, sensors, and software versions but usually do not provide a meaningful demonstration of Android key attestation. If the question is “what is inside my phone?”, a system-information utility is the better choice.
On the other hand, if the question is “what can Android’s keystore attest about a key on this device?”, a general diagnostic app is the wrong alternative. It may display security-related labels, but those labels are not a substitute for examining the attestation mechanism. This is where the demo earns its place: it addresses a narrow question that broad utilities tend to skip.
The friction comes from interpretation. I cannot recommend treating every field as self-explanatory, and a beginner may not know which values are important. The app is therefore more rewarding when used with a particular goal. Before opening it, I would write down the question I want answered. That simple step keeps the session from turning into a confusing tour of technical output.
There is also a trade-off between convenience and trustworthy validation. A developer might be tempted to make a client-side decision based on what the app displays. In a real service, I would not rely on a value merely because it appeared in a local interface. The server should validate signed evidence according to the project’s security policy. The demo can teach that distinction, but it cannot design the policy for me.
Its age rating of Everyone and free price make experimentation easy, and the app has passed the threshold of over one hundred thousand installs with a 4.8 average from around three hundred ratings. Those figures suggest that it has found a real audience among people interested in this specialized Android feature, but popularity should not change how narrowly I judge it: its success depends on whether I need Key Attestation specifically.
The release date of April 1, 2020, also gives useful context. This is not presented as a fashionable all-purpose security suite. I see it as a focused demonstration that belongs in a developer’s toolkit when the underlying Android feature is relevant. For a production project, I would still check current Android guidance and test on the devices I intend to support rather than assuming that a demonstration alone covers every modern requirement.
Who gains the most from installing it
The clearest audience is Android developers working with authentication, protected credentials, device trust, or any workflow where a server may need cryptographic evidence from a client. Security students and technically minded testers are also likely to benefit because the app turns a difficult system feature into something that can be explored directly.
I would especially recommend it to someone who has read about Android Keystore but has never seen attestation information produced on a real phone. The app can serve as a bridge between theory and implementation. It is also useful before a team commits to a device-trust design, because testing several phones early may expose assumptions that would otherwise surface much later.
There are cases where I would skip it. If I only need battery statistics, storage information, sensor testing, or a simple list of system specifications, this is too narrow. If I want a one-tap privacy score, it is also not the right tool. And if I am building a serious security product, I would not use the demo as a substitute for code review, backend verification, threat modeling, or testing against the actual deployment environment.
For everyday use, I would keep it installed only while investigating a project or learning Android security. It is not an app I would expect to open during a normal commute or use as part of a daily routine. That is not a criticism so much as an honest description of its design: the value is concentrated in a technical moment.
My final recommendation is therefore conditional but positive. Key Attestation Demo is a worthwhile free utility when the Android Key Attestation capability is the question in front of you. It gives developers and learners a practical reference point, encourages better thinking about cryptographic evidence, and compares favorably with generic device-information tools for this one purpose. Install it for investigation, not reassurance. Used with documentation, recorded test conditions, and proper server-side validation, it can turn an obscure Android security feature into something much easier to understand and apply responsibly.
Pros
- Open-source code makes its attestation process easier to inspect.
- Useful for developers testing Android hardware-backed security features.
- Displays detailed attestation certificate data for technical analysis.
- Helps compare device security capabilities across different Android phones.
- Small, focused app with no unnecessary social or entertainment features.
Cons
- Requires a compatible Android device to provide meaningful attestation results.
- Results can be difficult to understand without Android security knowledge.
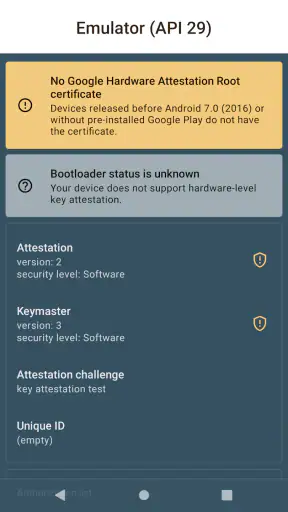
- Some devices may lack supported hardware-backed key storage.
- The demo does not replace a complete production security implementation.
- Limited usefulness for everyday users who do not develop Android apps.
FAQs for Key Attestation Demo
What is Key Attestation Demo used for?
Key Attestation Demo is a technical utility designed to demonstrate Android’s hardware-backed key attestation capabilities. It helps users and developers inspect how cryptographic keys are generated and verified through Android Keystore and related security services. The app is mainly educational and diagnostic, so it is more useful for developers, security researchers, and advanced Android users than for everyday phone owners.
Does Key Attestation Demo require root access?
In most cases, Key Attestation Demo is intended to work on a standard, non-rooted Android device, because it demonstrates APIs provided by the Android operating system and secure hardware. However, the results can vary depending on the phone model, Android version, available security hardware, and Google Play services configuration. Rooting, custom ROMs, or modified system software may reduce the reliability of the attestation results.
What information can the app show about my device?
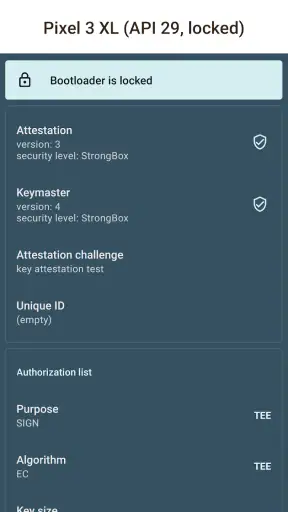
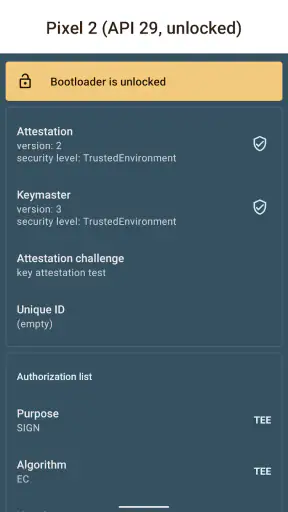
Depending on your device and Android version, the app may display technical attestation details such as key properties, certificate information, security levels, verified boot status, and other integrity-related values. These results are intended for analysis rather than general identification. Users should still review the permissions and privacy information before installing, since diagnostic tools can process device and security metadata while performing their tests.
Will Key Attestation Demo prove that my phone is completely secure?
No. The application can demonstrate specific aspects of Android’s key attestation and device integrity mechanisms, but it cannot guarantee that a phone is entirely secure. Attestation results are influenced by hardware support, firmware, operating-system updates, bootloader status, and service availability. A successful result should be treated as one security indicator, not as a complete security audit or protection against every type of attack.
Why might the attestation test fail or show limited results?
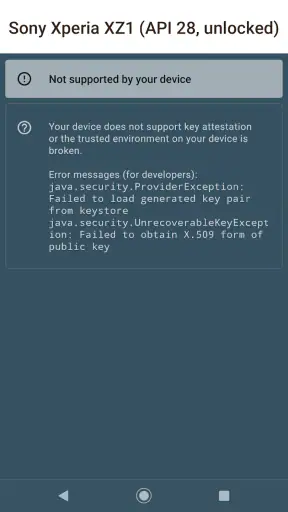
A test may fail or provide incomplete information when the device lacks supported secure hardware, uses an older Android release, has an unlocked bootloader, runs a custom ROM, or cannot access required Google services. Temporary network problems and manufacturer-specific limitations can also affect the output. If results look unusual, update the system, use the official firmware, and repeat the test before drawing conclusions.











